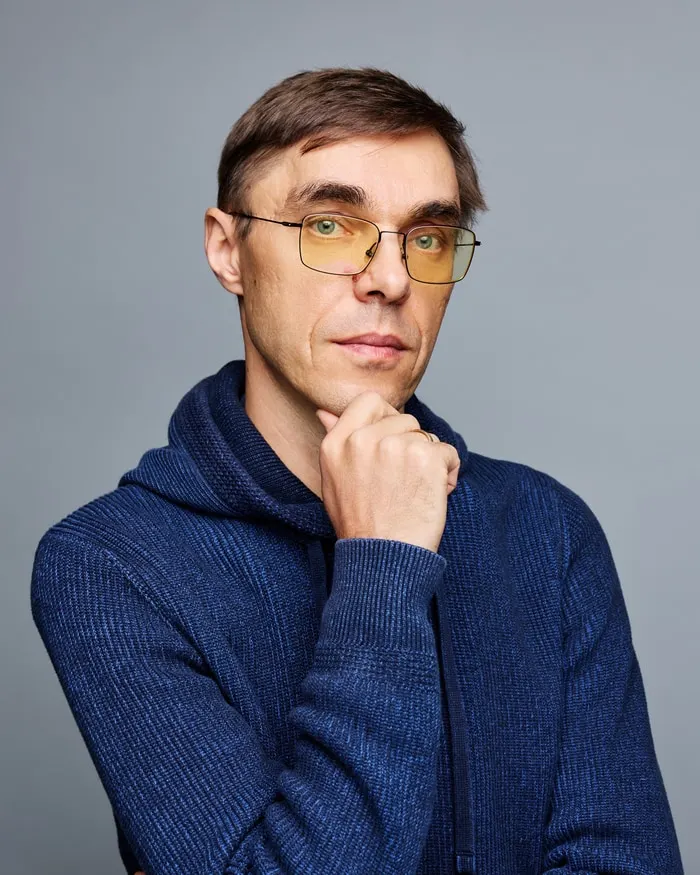
Secure AI on Azure
AI Foundry and Fabric landing zones with private networking, managed identity, data-exfiltration controls and auditable RBAC — architected so that adopting AI does not widen the attack surface.
Available for advisory engagements, architecture reviews and workshops
I design secure, large-scale Azure platforms — and the governance that keeps them compliant once AI workloads land on them.
Cloud & Security Architect · Tampa, Florida — working globally, remote-first
About
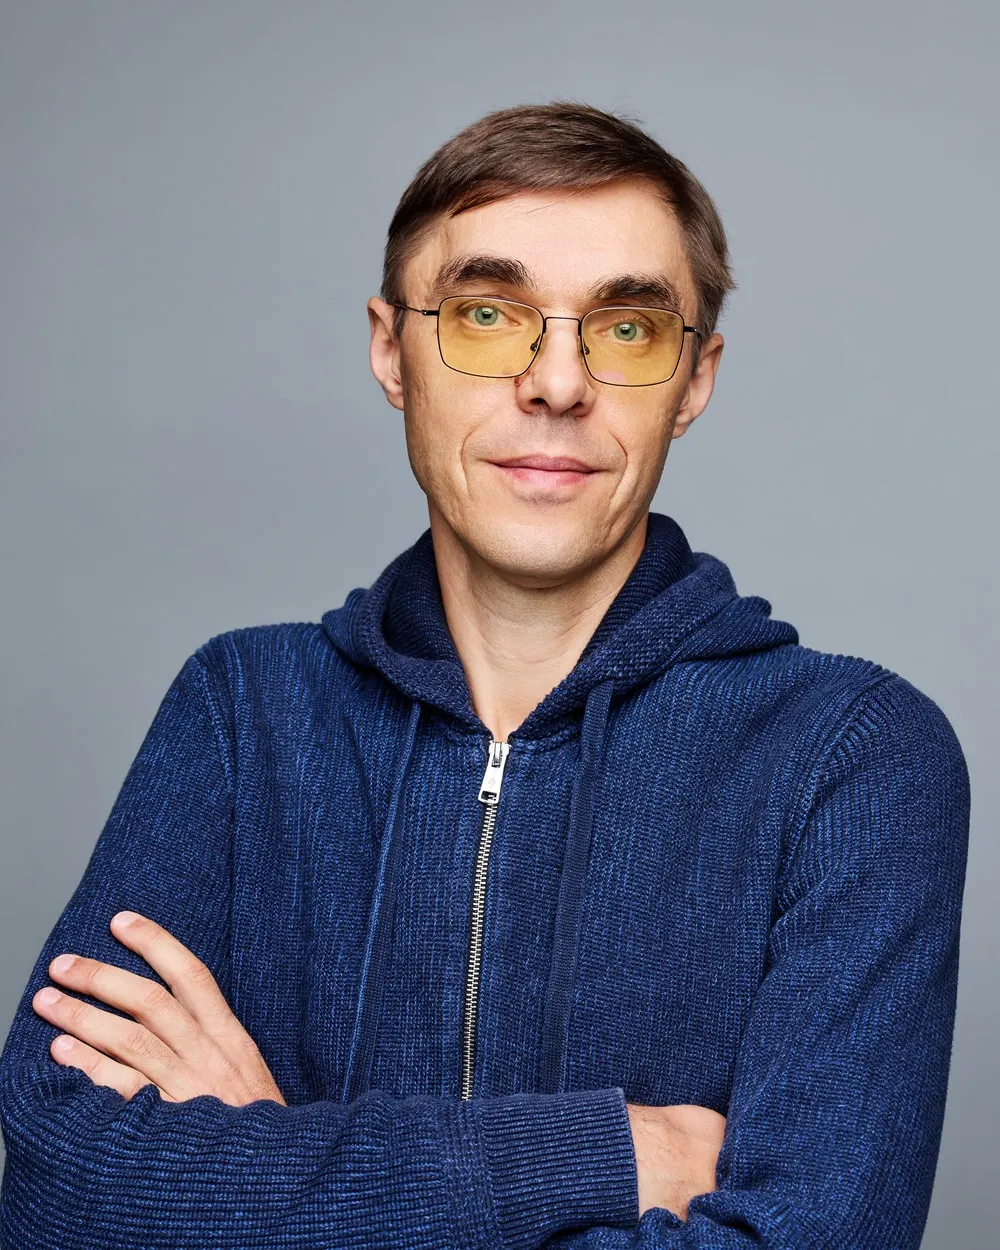
Twenty years of building the platforms that regulated organisations actually run on — now focused on the security and governance problems that AI adoption creates.
Infrastructure, cloud and security architect with 20+ years of experience delivering large-scale, secure and cost-efficient technology platforms for international organisations.
I work at the intersection of three things that rarely sit together well: enterprise-grade Azure architecture, regulatory compliance, and production AI. My engagements typically involve designing landing zones that satisfy auditors and enable data science teams at the same time — private networking, identity governance, policy-as-code and the operational evidence to prove it all works.
I have led organisations to ISO/IEC 27001 certification, designed GPU-enabled ML platforms, rebuilt enterprise network topologies for 10x growth, and delivered infrastructure cost efficiencies measured in millions.
Jury appointment
Member of the Jury, Cybersecurity competition — IT-Universe 2026
International Student IT Olympiad IT-Universe
Peer-reviewed publication
A model for automated identity and access management in enterprise cloud systems
Science and Technology Today
DOI 10.52058/2786-6025-2026-2(56)-2323-2335
In the press
The Ukrainian who built the "most advanced" technology platform for a European AI company
Gazeta.ua
Memberships
How I help
Engagements usually start as an architecture review and turn into a delivery programme. These are the problems clients bring me in for.
AI Foundry and Fabric landing zones with private networking, managed identity, data-exfiltration controls and auditable RBAC — architected so that adopting AI does not widen the attack surface.
Defender coverage, ingress security with NVA/WAF, SOC integration at scale, PIM/JIT access models and policy-as-code guardrails across an enterprise tenant.
Translating ISO/IEC 27001, NIST CSF 2.0, GLBA and FFIEC expectations into enforceable technical controls, version-controlled change management and audit-ready evidence.
Tiered Terraform and Bicep module architectures, blue-green and canary release automation, and Azure DevOps pipelines that give developers velocity without loosening the guardrails.
Selected work
A selection of architecture and delivery work. Open-source implementations and detailed write-ups are being published progressively.
An agent that investigates production incidents on its own, at a median cost of $0.36 per investigation.
A hosting platform for models and agents that keeps AI inside the corporate security boundary.
Identity objects declared in git, applied by pipeline, with no standing privilege in the tenant.
Kubernetes platform for machine-learning workloads that cut $1.7M in annual operating expenditure.
An 8x reduction in log storage cost by moving high-volume telemetry to ADX clusters.
Tenant-wide log and security-data collection exposed to a third-party SOC in real time.
Declarative, Git-backed RBAC across an entire Azure tenant — access reviews become automatic.
Took IT operations from ad-hoc to certified, enabling a multimillion-dollar transaction.
Developer freedom in tier 2, hard guardrails in tier 1 and tier 0 — enforced by module topology.
Blue-green for Azure services that do not support it natively — container apps and static web apps.
A multi-agent pipeline for IaC migration that saved over 90% of the conversion effort.
A Virtual WAN topology designed to absorb 10x growth without redesign.
Request-level visibility across NVA, NSG, gateway and sidecar — analysed as big data.
Technology
Depth in the Microsoft platform, with the surrounding cloud-native and security tooling that enterprise environments actually require.
Credentials
Microsoft Certified
CNCF · Linux Foundation
Microsoft Certified
Microsoft Certified
Microsoft Certified
Microsoft Certified
Microsoft Certified
Microsoft Certified
CNCF · Linux Foundation
CNCF · Linux Foundation

HashiCorp

Bureau Veritas
Earlier certifications
Hobbies
Two things that keep me curious once the laptop is closed.
Travel
From Magadan to Hawaii — 91 places I have been, each with its flag on a glass globe you can spin, zoom and replay.


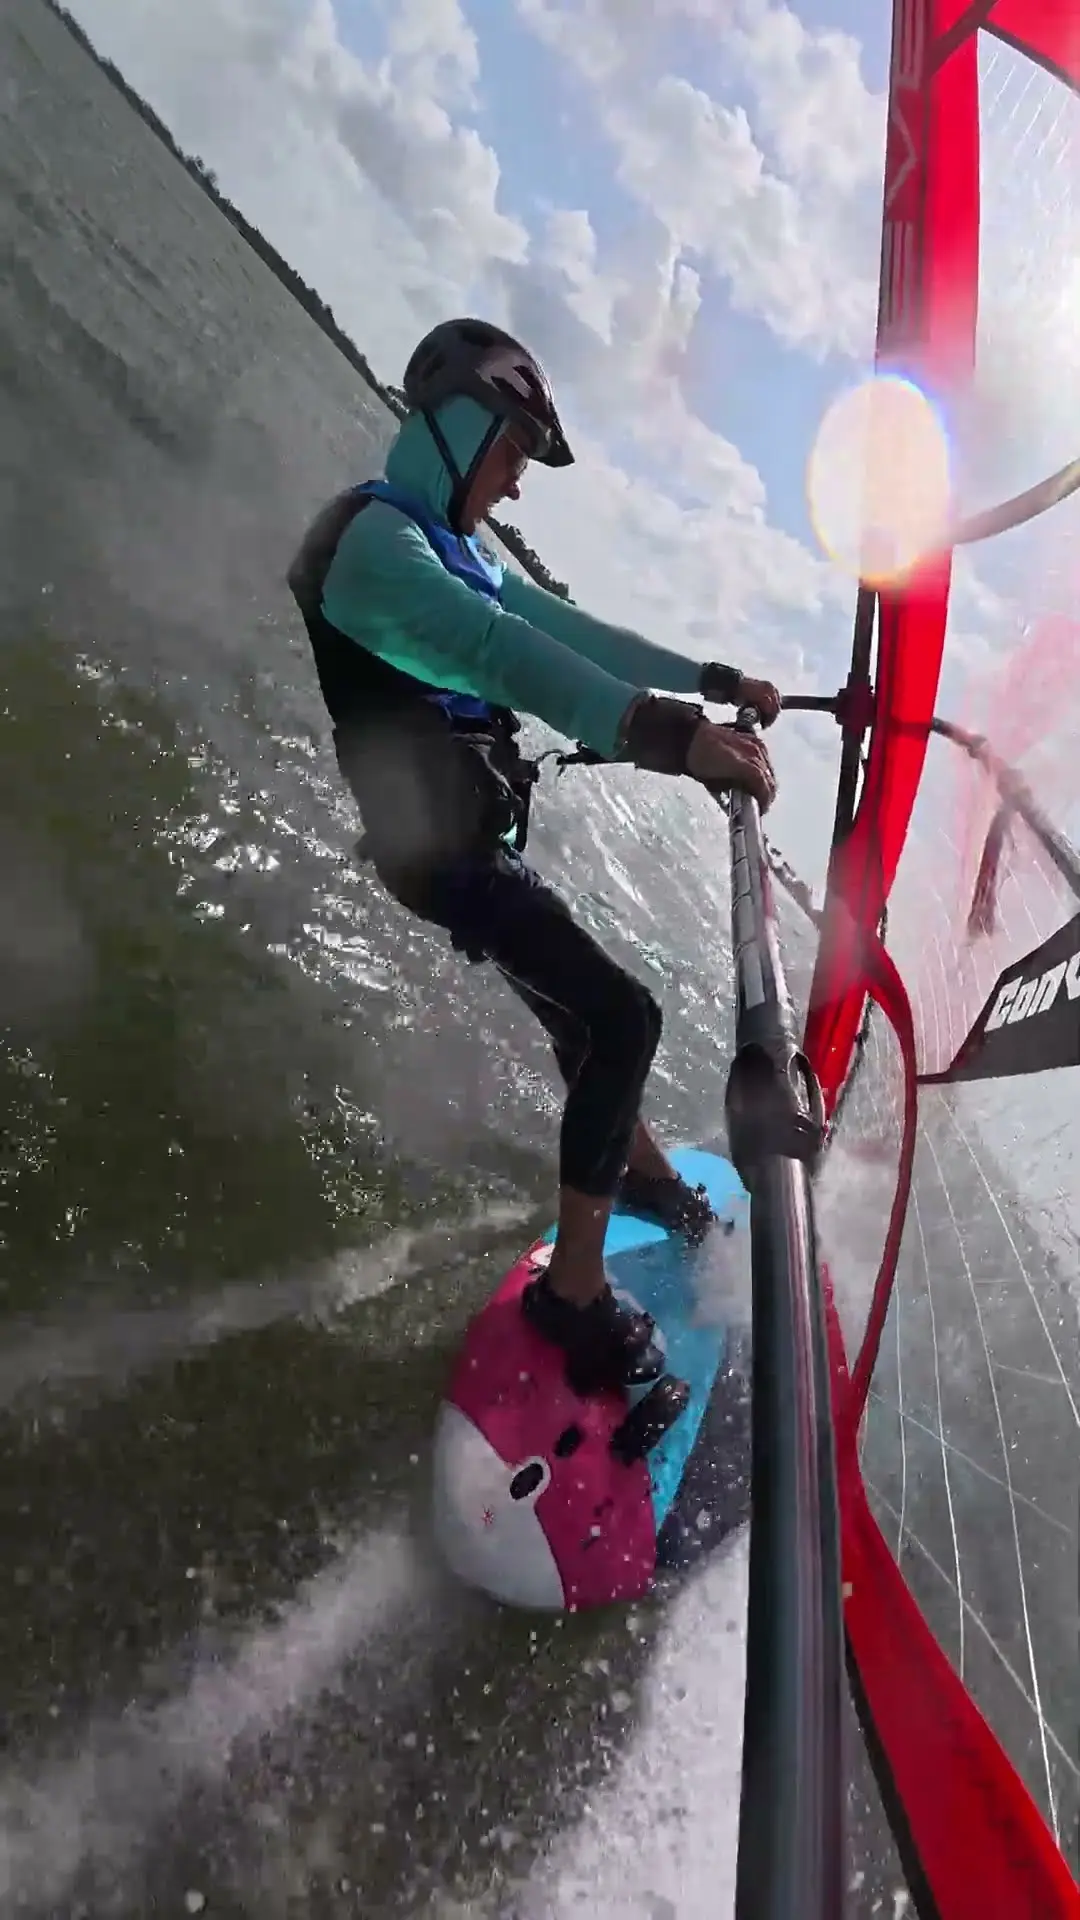
Windsurfing
When the wind picks up, I am out on the water.
Contact
I take on a small number of advisory engagements, architecture reviews and workshops at a time. If you are designing an Azure platform that has to be secure, compliant and fast to move on, let's talk.
Tampa, Florida — working globally, remote-first